
Kempinski has been informing guests over the past 24 hours about a significant data breach.
The hotelier warns that emails and WhatsApp messages may ask you to confirm your stay or even make a payment and that these are all fraudulent.
You can access Kempinski here.
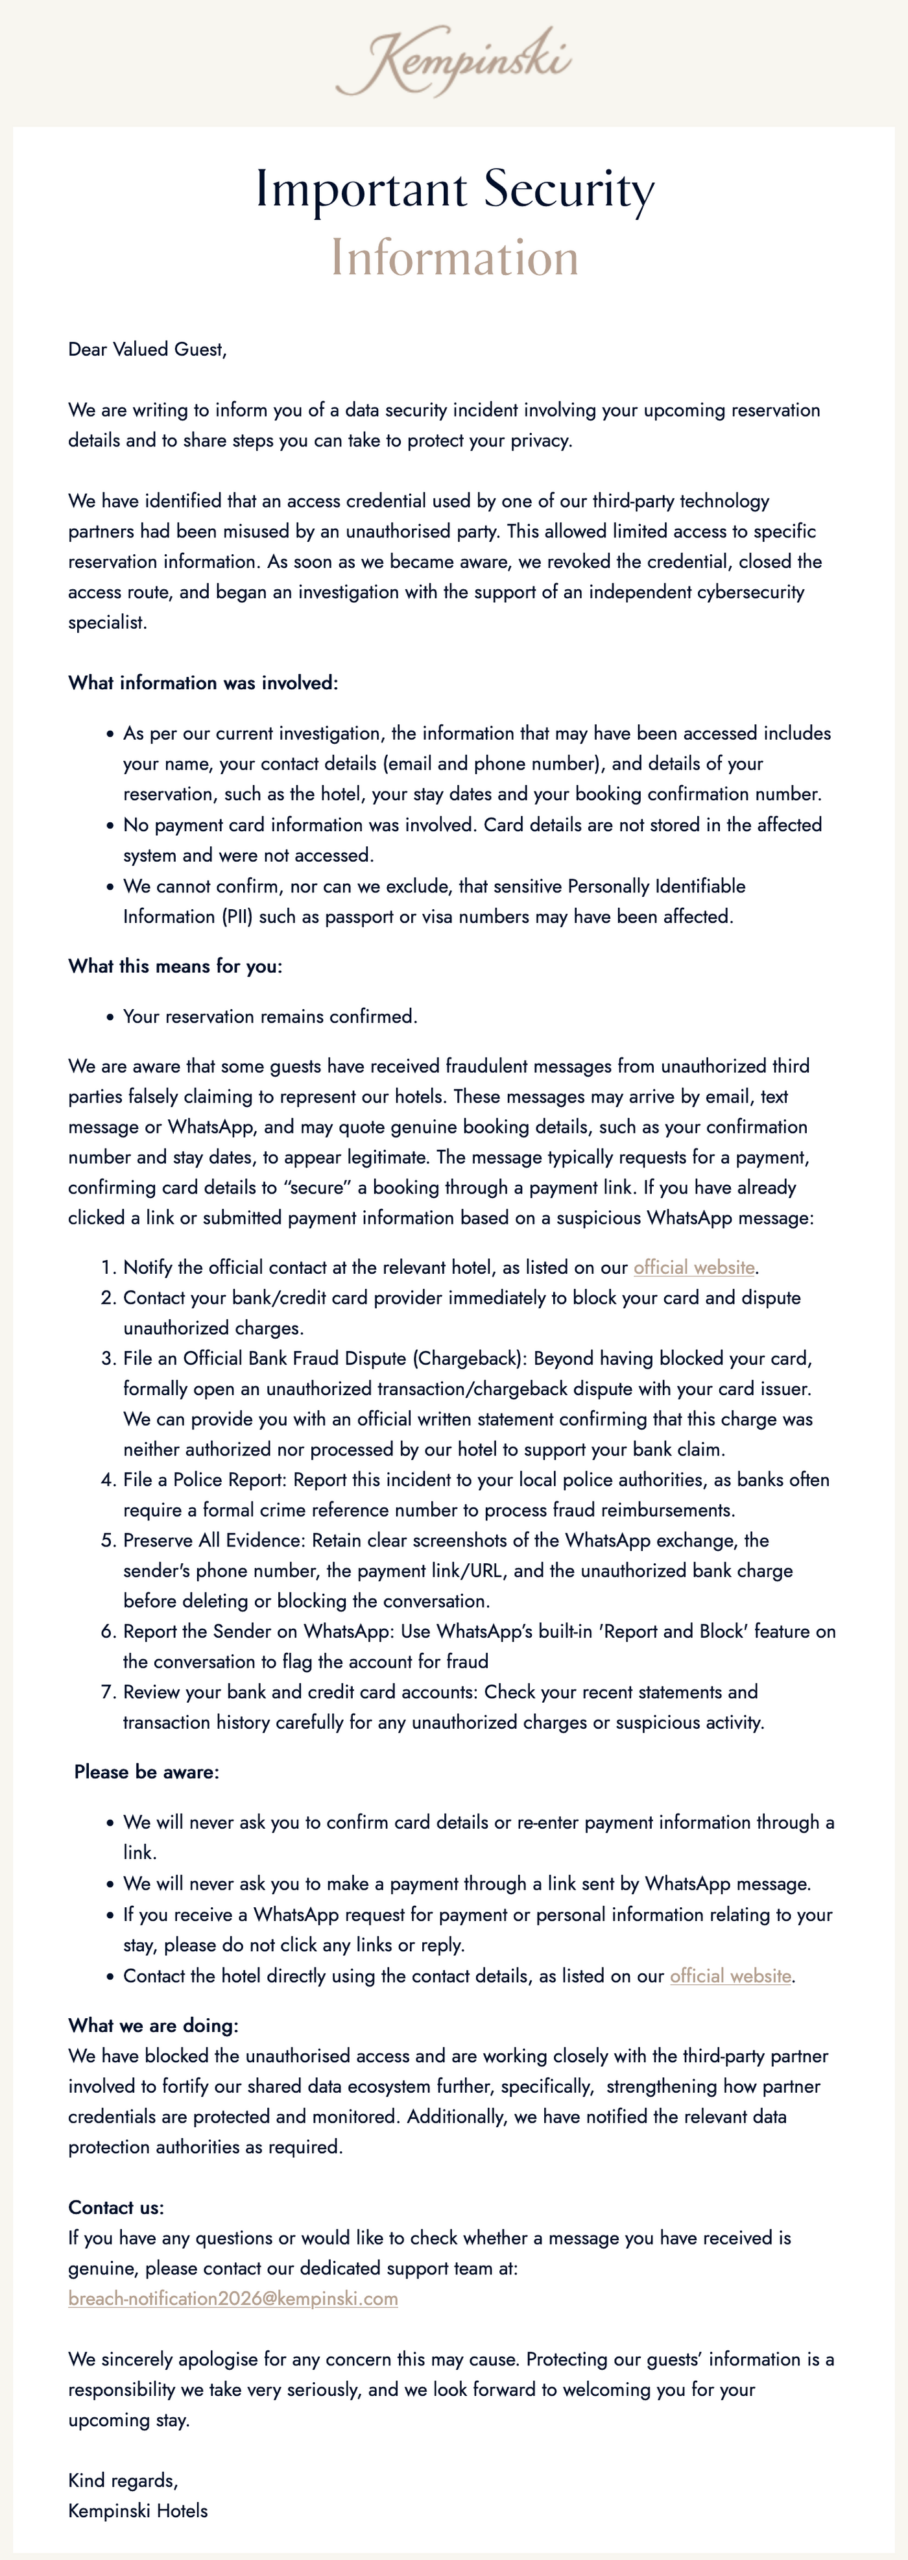
Information Compromised: Full name Contact details (email address and phone number) Reservation specifics (hotel property, stay dates, and booking confirmation number)
Payment information has not been leaked, but the hotelier is not sure if other sensitive information such as passport, ID, or visa numbers have gone out of the door as well:
“We cannot confirm, nor can we exclude, that sensitive Personally Identifiable Information (PII) such as passport or visa numbers may have been affected.”
Phishing Scams
Guests with upcoming Kempinski reservations will likely be inundated with emails and WhatsApp messages requesting they confirm the booking and make a prepayment. These are all fraudulent.
Kempinski’s Email to Affected Guests:
Conclusion
It is unfortunate that businesses cannot safeguard data that thieves can then use to get cash from unsuspecting travelers.
It doesn’t help that you sometimes receive links from hotels asking for a payment, and you can NEVER be sure that these are legit, and I always refuse.
Even if the email appears to come from the company in question, there is no way to verify that the payment link is legitimate.
There have been several cases from Booking.com, Accor, and other bookings that have been affected by scams like this.